AI touches your business in four places
Every AI initiative comes down to the same four surfaces. Govern all four, and you've covered how AI actually shows up, not just the tools everyone's already talking about.
Users
Every AI app your people reach for, sanctioned or not, with visibility down to the individual account.
Self-hosted models
Models you've built or fine-tuned yourself, where no public vendor is hardening it for you.
Agents
AI agents acting on your behalf, and the tools and servers they connect to.
Data
What feeds every prompt, model and agent, discovered and classified before it's exposed.
Security was built for humans. AI doesn't work like one
Cybersecurity has always centred on three questions: who has access, are systems hardened, and are threats detected. That was enough when a person sat behind every action. AI tools, and increasingly AI agents, now take actions of their own, deciding what to open, what to send, and where, often faster than anyone is watching.
Control the door
Govern the action
Security teams are already telling researchers this shift is underway: in one 2026 McKinsey survey of cybersecurity buyers, roughly three-quarters were seeking better protection against AI input manipulation, and close to a third said they weren't confident their current vendors could deliver it.
Source: McKinsey survey of cybersecurity buyers, 2026.
How we can help
Powered by Netskope's Skylight, AI controls are deployed as part of the platform you already run, not a separate console.
AI Command Center
Every user, app, agent, model and AI interaction inventoried continuously, feeding one picture instead of disconnected tools.
GenAI App Security
Data loss prevention purpose-built for prompts, uploads and generated output, not retrofitted from web filtering.
Agent Action Control
Classifies what an agent is about to do by risk, and blocks the action, such as deleting a repository, before it executes.
Agentic Broker
Assesses the risk of the tools and servers an agent connects to before it's allowed to trust them.
AI Gateway & Guardrails
Authenticates and rate-limits every call to a self-hosted model, with guardrails moderating prompts as volume scales.
AI Red Teaming
Automated adversarial testing runs malicious prompts against your models to find the gap before someone else does.
The same problem, a different face in every sector
AI governance looks different depending on what you're protecting.
Our Credentials
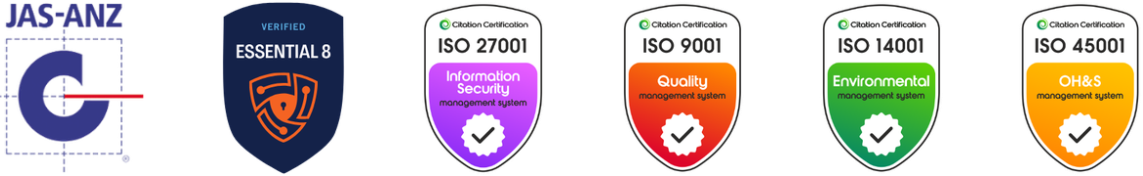
Independently audited against the standards your procurement team and your tender documents will ask for.
Tell us where your rollout stands
Scoping a deployment, mid-rollout with another provider, or starting again after a stalled project. We'll give you an honest read on what it takes to get it done.