Managed Security Service Edge (SSE)
One platform, instead of a patchwork
SSE converges the security services a business used to buy separately, from separate vendors, into one platform with one policy engine. Instead of a web gateway from one provider, a CASB from another and a VPN from a third, all trying to talk to each other, everything runs through a single point of control.
Organisations with a hybrid workforce, cloud-first applications, and data that no longer sits behind a single network perimeter. If your people work from anywhere and your applications live in the cloud, SSE is the layer that secures the connection between them.
Legacy, perimeter-based tools protect the network. They were never built to protect data itself, wherever it happens to be accessed from. SSE moves the security control to the data and the user, not a location on a map.
Next Gen Secure Web Gateway
Cloud-delivered web security protecting websites, SaaS apps and data for any user, on any device, anywhere.
Cloud Access Security Broker
Identifies and manages use of managed and unmanaged cloud apps, covered in full below.
Zero Trust Network Access
Replaces legacy VPNs with secure, identity-based access to private and legacy applications.
Firewall as a Service
Network security on outbound traffic, across every port and protocol, for users and offices alike.
Remote Browser Isolation
Isolates risky websites for safe viewing, so a bad click doesn't become an incident.
Data Loss Prevention
Contextual, inline protection that stops sensitive data leaving through web and cloud traffic.
Managed Cloud Access Security Broker (CASB)
Confidently adopt cloud apps, without losing control
Any organisation whose staff use cloud and SaaS applications, sanctioned or not, including personal instances of apps you've already approved. If you can't currently tell a corporate Google Drive account from someone's personal one, CASB is the gap it closes.
The biggest risk in cloud adoption isn't the app itself, it's the inadvertent or deliberate movement of sensitive data between corporate and personal accounts, or into services nobody in IT knows are being used. CASB gives you the visibility and the fine-grained control to stop that, without blanket-blocking the tools your people rely on.
Cloud app risk scoring
Every new SaaS and AI application in use is automatically discovered and risk-rated, not just the ones IT already knows about.
Advanced data loss prevention
Contextual scanning across email, chat, file sharing and web forums stops sensitive data leaving in real time.
Granular visibility and control
Policy by user, app, instance, risk and activity, not a blunt allow-or-block for the entire service.
Real-time policy enforcement
Inline protection stops data loss and threats as they happen, not after the fact.
Source: Netskope Cloud and Threat Report, 2026.
Managed Data Security Posture Management (DSPM)
Answer the three questions that actually matter
Where is all your data? What is the nature of that data? Who has access to it? Most organisations can't answer these with confidence, across cloud, on-premises and hybrid environments, until something goes wrong. DSPM gives a continuous, real-time answer instead of a point-in-time audit.
Comprehensive visibility
A full view of structured and unstructured data across every environment, including data you didn't know existed.
Proactive risk management
Misconfigurations and vulnerabilities identified before they become the reason for an incident review.
Automated compliance
Policies aligned to standards like GDPR and HIPAA, simplifying audits instead of scrambling for them.
Reduced attack surface
Data access and interactions controlled and limited across the whole infrastructure, not just the obvious parts.
Managed Email Security
An overlay on Google Workspace and Microsoft 365, not a replacement
Material sits on top of the productivity suite you already run, closing the gaps that native controls and legacy gateways leave open. Deployed by API, in minutes, with nothing to reroute your mail flow through.
Organisations running Google Workspace or Microsoft 365 who need protection beyond what the platform provides natively, particularly where email is the most likely way in and the mailbox holds years of sensitive history nobody's reviewed.
Modern attacks span email, identity, data and connected apps in one chain. Defending any single layer in isolation leaves the rest exposed.
Email security
Catches the phishing and BEC attacks that native filters and legacy gateways miss, with automated user-report triage.
Account takeover containment
Redacts sensitive messages and locks down message-level access the moment credentials are compromised, before an attacker can reset a password.
OAuth and agent governance
Real-time visibility into what every connected app and AI agent is actually doing with the access it's been granted, not just when it was granted.
File security
Finds sensitive files shared too broadly in Drive and remediates in bulk, without interrupting the people who legitimately need them.
Sources: SlashNext; Material Security Research, 2026; IBM Cost of a Data Breach Report, 2025.
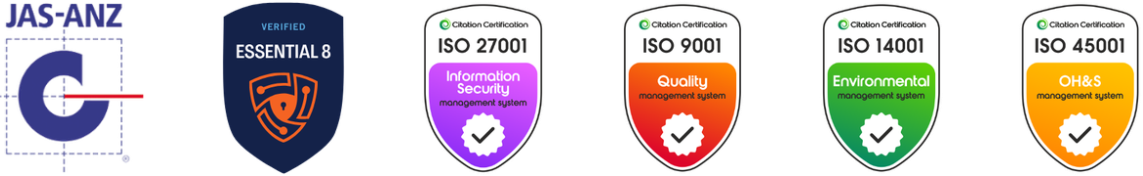
Our Credentials
Independently audited against the standards your procurement team and your tender documents will ask for.
Tell us where your rollout stands
Scoping a deployment, mid-rollout with another provider, or starting again after a stalled project. We'll give you an honest read on what it takes to get it done.